- Home
- Warden Liaison
Warden Liaison
Who accesses what,in real time.
Warden Liaison is a security solution that gives a real time view of access management. Every action carries a user or an agent, a security group and a role.
Built for large teams. Within reach of every team.
- Live access
- Groups and roles
- Credential vault
- API manager
- Hardware security keys
- Hosted in Canada

Warden Liaison console, Live access screen (French interface). Sample data.
The problem
Access grows faster than anyone can track it.
The bigger a team gets, the more passwords, API keys and portals it collects. Without an overall view, nobody can say who has access to what, or who did what.
Shared credentials
Passwords travel by email, chat or spreadsheet. When someone leaves the team, nobody knows what they still know.
Portals with no API
Many suppliers only offer a web portal. Repetitive tasks are done by hand, often with a shared account.
No clear trail
When an invoice is downloaded or a setting is changed, it is hard to know who did it, in what capacity and with what approval.
Live access
Every event carries a group and a role.
The access feed shows, live, who, user or agent, is accessing which portal, credential or API. Every event shows the security group and the role of the person or agent.
- User or agent, portal, credential or API
- Security group and role on every event
- Approvals visible in the feed
- Instant revoke from the console
- Hardware security key events
- Audit log of every action
Live access
Illustrative example. Names and actions are fictitious.
Security groups and roles
Clear rights, by group and by role.
Every person and every agent belongs to a security group and has a role. Rights follow the role, not someone’s memory.
Roles
- AdministratorConfigures groups, roles, the vault and APIs.
- ApproverApproves or declines access requests and sensitive actions.
- OperatorUses the portals and credentials their group allows.
- Read onlyViews the feed and the log, without changing anything.
- AgentRuns defined tasks on named portals, within a set scope.
Example groups
- Finance
- Operations
- IT
- Leadership
- Automated agents
Groups are defined with you, to match your organization.
- ApprovalsA sensitive action waits for an approver.
- Instant revokeAccess, a session or a key is withdrawn in one step.
- SSOSign in with your organization’s identity provider.
- Audit logEvery action is kept with who did it, their group and their role.
Physical authentication
A physical key for the actions that matter.
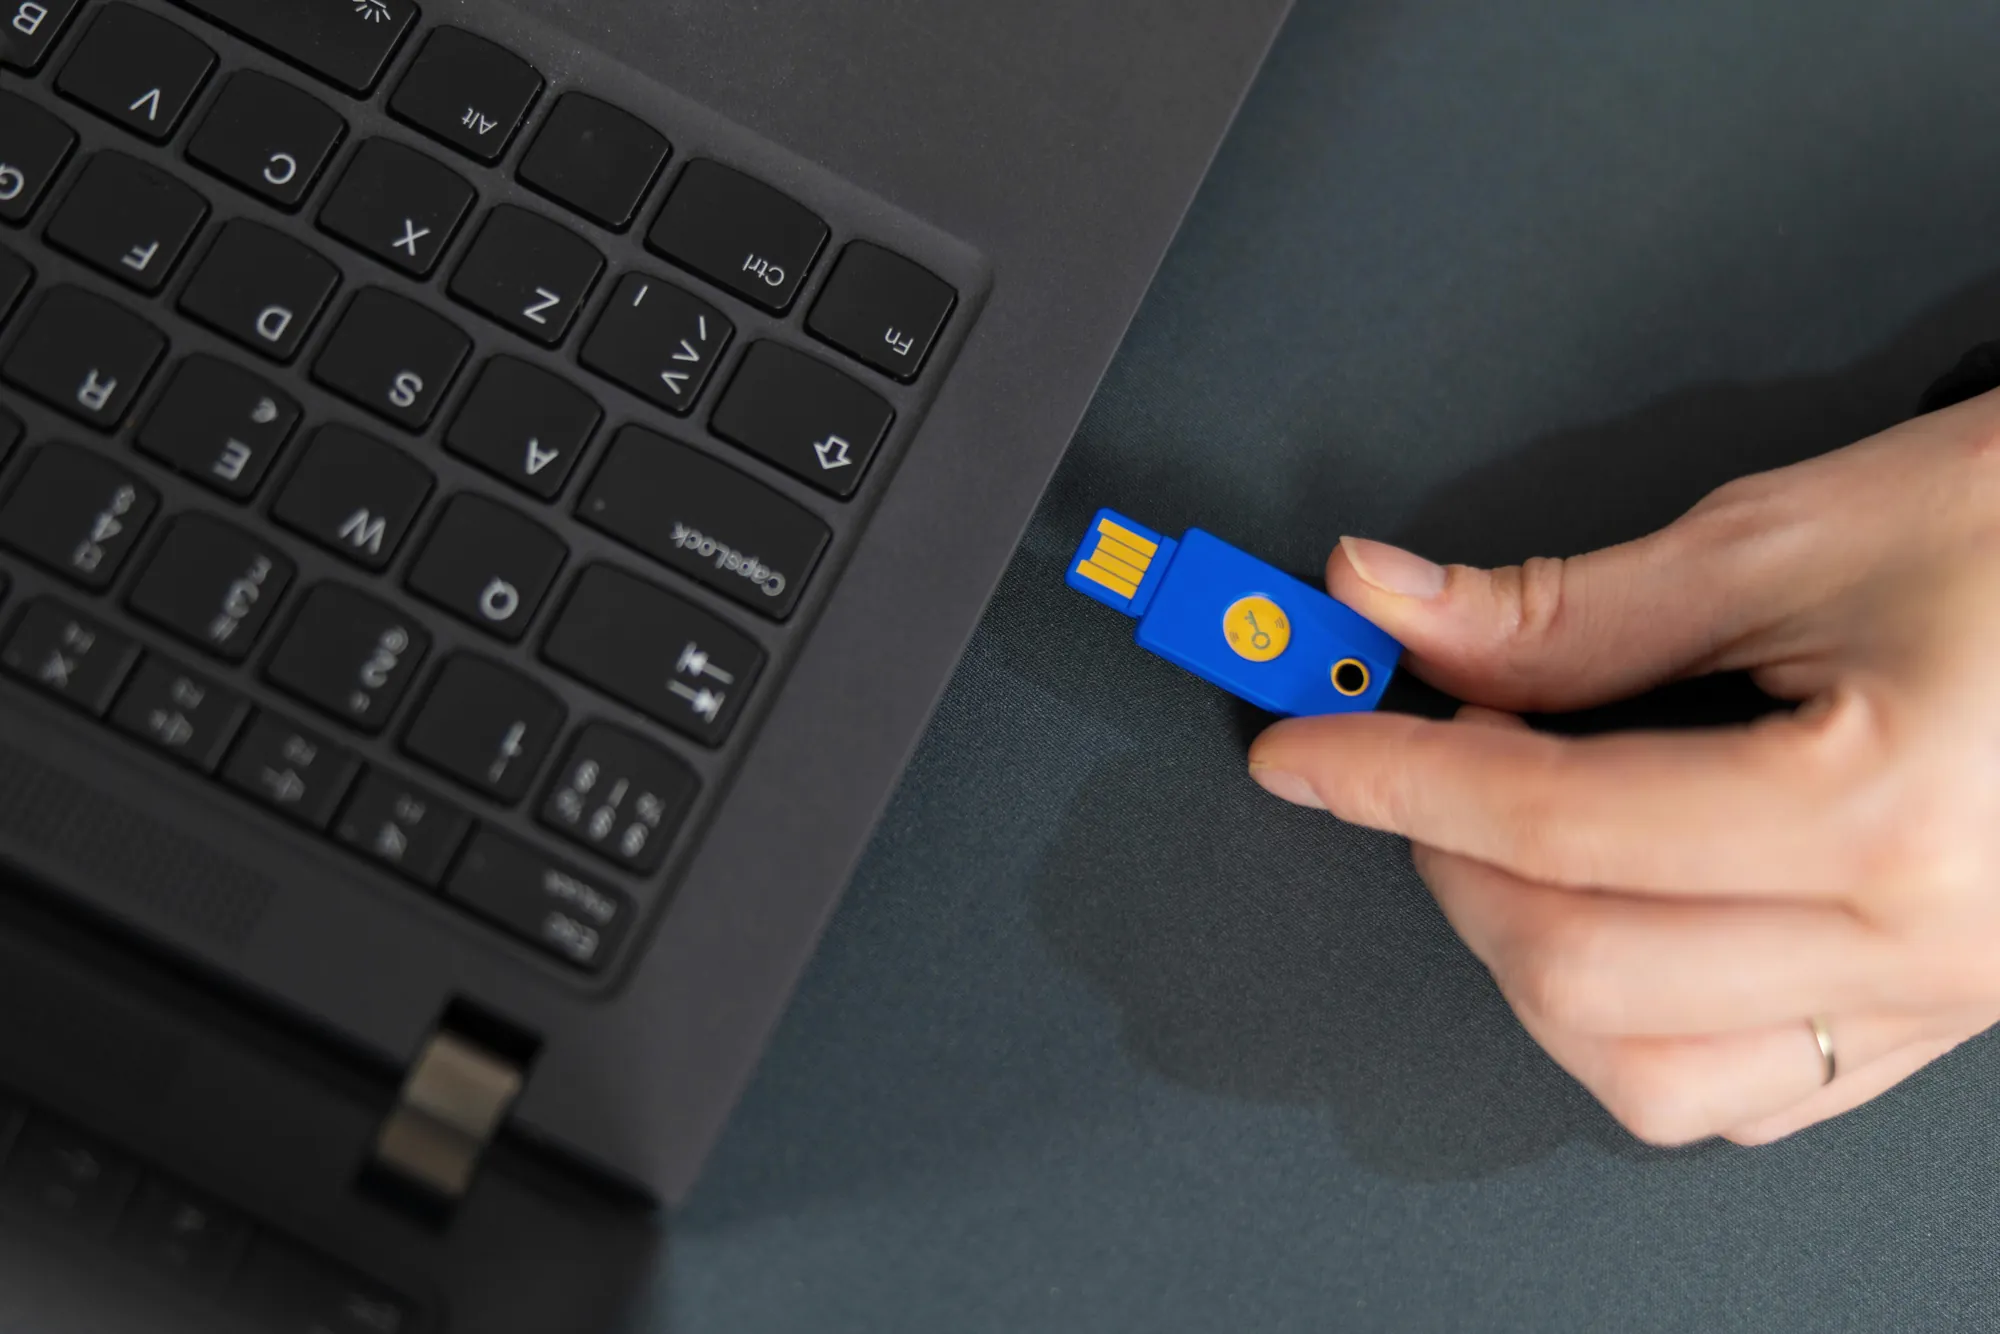
Warden Liaison supports physical authentication with hardware security keys such as YubiKey (FIDO2, WebAuthn, passkeys). A stolen password is no longer enough.
- Required by group or roleA hardware key can be mandatory for a security group or a role, for example Finance or Administrator.
- Enrollment and inventoryEach member enrolls their key. The inventory shows which keys belong to whom.
- Lost key, revoked keyA lost key is revoked immediately from the console.
- Step up for sensitive actionsOpening the vault, approving or revoking can require a touch on the physical key.
- Visible in the feedKey events appear in the live access feed, with group and role.
YubiKey is named as an example of a compatible key. No partnership is implied.
Vault and API
Secrets stay in the vault.
Credentials and API keys are managed in one place, by group and by role.
Secrets are injected without being shown.
- Passwords, tokens and keys kept in the vault
- Injected at the moment of access, never shown to the user or the agent
- Vault access by group and role
- Every use recorded in the audit log
Your API keys, under control.
- API keys managed in one place
- Key rotation
- Rate limits per key
- Endpoint catalog
Agents
No API? Liaison uses the portal.
When a supplier only offers a web portal, a Liaison agent signs in and runs the agreed task: downloading invoices, retrieving statements, checking shipment tracking.
How it works
From the first portal to the whole team.
Every rollout follows the same steps, agreed with you.
Contact sales01
Discovery
Together we map your portals, credentials, APIs and teams.
02
Setup
Security groups, roles and the credential vault are put in place.
03
Pilot
A pilot on named portals, with a defined team.
04
Deployment
Extension to other teams and portals, at your pace.
Security and residency
Your access and your logs stay in Canada.
The Warden Liaison console, credential vault and logs are hosted in Canada.
- HostingConsole, vault and logs hosted in Canada.
- SecretsInjected without being shown, to users or agents.
- Sign inSSO with your organization’s identity provider.
- AuthenticationFIDO2 and WebAuthn hardware security keys, required by group or role.
- ControlApprovals and instant revoke.
- TraceabilityAudit log of every action, with user or agent, group and role.
Warden Liaison provides verifiable controls and records. It is not a compliance certification.
Use cases
By department.
The same controls serve every department, each with its own groups, roles and portals.
Finance
Invoices, bank statements, accounting software: access to financial portals is approved, logged and revocable.
Operations
Supplier portals and internal tools open by group and role, with no shared passwords.
Logistics
Shipment tracking on carrier portals is done by a person or an agent, with a record of every lookup.
IT
One view of access, the vault and API keys, with key rotation and instant revoke.
Questions
Frequently asked questions.
Do our suppliers need to offer an API?
Do users see the passwords?
Where is our data hosted?
Is Liaison only for large companies?
Can access be removed immediately?
Does Liaison support hardware security keys?
How does a project start?
Does Liaison replace a compliance certification?
See your access in real time.
Tell us about your teams, portals and credentials. We will propose a discovery, then a pilot on named portals.
Warden Liaison. Operational security.